FBI launches investigation into suspected breach of National Crime Information Center database
The FBI is probing a possible intrusion of its NCIC criminal database after reports of a breach, amid a series of recent U.S. tech outages and prior hacking incidents involving the agency.
By LAS News Desk · Published 21 Nov 2026, 11:15 WAT
The Federal Bureau of Investigation has opened an inquiry into a reported breach of its National Crime Information Center (NCIC) database, according to two sources briefed on the matter. The NCIC system, which stores warrants, background checks and other critical data for federal and local law enforcement, is a core component of U.S. public safety infrastructure. The BBC has sought comment from the FBI but has not yet received a response.
The alleged intrusion comes at a time when the United States has experienced a wave of technology disruptions across multiple sectors, including banking and air‑traffic control, during the previous week. While officials have publicly denied that those outages resulted from cyberattacks, the incidents have intensified scrutiny from lawmakers and heightened concerns about the resilience of critical digital systems.
Background
The NCIC database has long been a target for cyber‑criminals, with the FBI previously confirming investigations into attacks by the hacking collective known as ShinyHunters. In September, the bureau disclosed that ShinyHunters claimed to have exfiltrated personal data on approximately 38,000 FBI employees. A former FBI agent later expressed fears that current staff could be at risk if their personal information were to be published online, potentially exposing them to criminal or hostile nation‑state actors.
The current investigation follows that earlier episode and coincides with other reported cyber incidents. NBC reported an apparent cyberattack on the United States Department of Agriculture’s farm payment system, though the USDA has not issued a public statement. Additionally, the White House recently dismissed National Cyber Director Sean Cairncross, with President Donald Trump stating that Cairncross was “not good enough,” a move that underscores the heightened political focus on cyber‑security challenges.
Why it matters
The NCIC database is integral to law‑enforcement operations nationwide, providing real‑time access to information on warrants, stolen property and missing persons. A compromise of this system could jeopardise investigations, endanger officers and civilians, and erode public confidence in the ability of agencies to protect sensitive data. Former FBI personnel have warned that exposure of employee details could facilitate targeted attacks against bureau staff, potentially disrupting internal security protocols.
Beyond the immediate risk to law‑enforcement personnel, the breach raises broader concerns for the private sector and the public, given the recent series of technology outages that have already strained financial services and aviation safety. Lawmakers have called for increased oversight and stronger cyber‑defence measures, reflecting a growing perception that critical infrastructure may be vulnerable to sophisticated hacking groups.
What happens next
The FBI’s investigation is ongoing, with officials yet to disclose the scope of the breach or any identified perpetrators. No official comment has been provided by the bureau, and the agency has not indicated whether any data has been confirmed as accessed or exfiltrated. The investigation will likely involve coordination with other federal cyber‑security entities, although specific next steps have not been detailed in the available reports.
Stakeholders, including law‑enforcement agencies that rely on NCIC data, are expected to monitor the situation closely while implementing any interim security measures advised by the FBI. The outcome of the probe may also influence forthcoming legislative discussions on cyber‑security funding and oversight, particularly in light of recent high‑profile outages and the recent dismissal of the National Cyber Director.
The situation remains fluid, and further updates are anticipated as the FBI progresses with its inquiry into the alleged NCIC breach.
Sources
Spotted an error? · Corrections policy
Related stories
US Agriculture Department and FBI suffer separate cyber breaches amid nationwide tech disruptions
Hackers accessed systems at the USDA and the FBI, prompting concerns over payment data and criminal‑information databases as the United States grapples with a series of high‑profile technology outages.
LAS News Desk · 22 Nov 2026, 10:15 WAT · 1 source
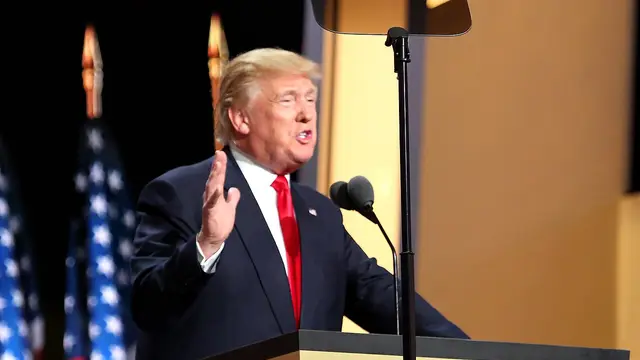
Trump administration appoints Pentagon CIO Kirsten Davies as acting national cyber director after Sean Cairncross departs amid tech outages
President Donald Trump has named Pentagon chief information officer Kirsten Davies as the acting National Cyber Director, replacing Sean Cairncross who left the post following a series of high‑profile technology failures that affected aviation, email and government networks.
Photo: Ali Shaker/VOA / Wikimedia Commons · Public domain
LAS News Desk · 20 Nov 2026, 17:45 WAT · 7 sources
Binance recovers 90% of $6.3bn stolen in record crypto hack, FBI attributes attack to North Korea
Binance says it has reimbursed most of the $6.3bn lost in the largest cryptocurrency theft on record, while the FBI blames a North Korean hacking group known as TraderTraitor for the breach.
LAS News Desk · 1 Nov 2026, 14:45 WAT · 10 sources
TFG London investigates cyber‑attack on Phase Eight, Hobbs and Whistles
The owner of Phase Eight, Hobbs and Whistles is investigating a cyber-attack that may have exposed customer data, with online orders paused as a precaution.
LAS News Desk · 10 Nov 2026, 07:27 WAT · 2 sources
France accuses Iran's Revolutionary Guards of unprecedented supermarket cyberattack
French authorities have attributed large-scale cyberattacks on supermarket refrigerators to Iran's Revolutionary Guards, vowing European sanctions and opening a criminal investigation.
LAS News Desk · 9 Nov 2026, 22:40 WAT · 8 sources
French blood banks thwarted cyberattack that targeted refrigeration systems
Three French blood banks experienced a cyberattack that raised temperature settings in their cold‑storage rooms, but staff moved supplies to unaffected units, preventing any loss of blood products.
LAS News Desk · 4 Nov 2026, 21:46 WAT · 3 sources
More Top news ›
- Andorra goalkeeper Owono banned for 12 matches after fatal collision with Tenerife striker
- US envoys announce EU participation in next Ukraine‑Russia peace round as Putin maintains hardline demands
- Murdaugh defense seeks dismissal of murder indictments citing investigator misconduct
- Thomas Markle returned to federal custody in Florida after alleged ankle‑monitor breach
- Russian missile and drone strikes injure nine and damage Ukraine power grid